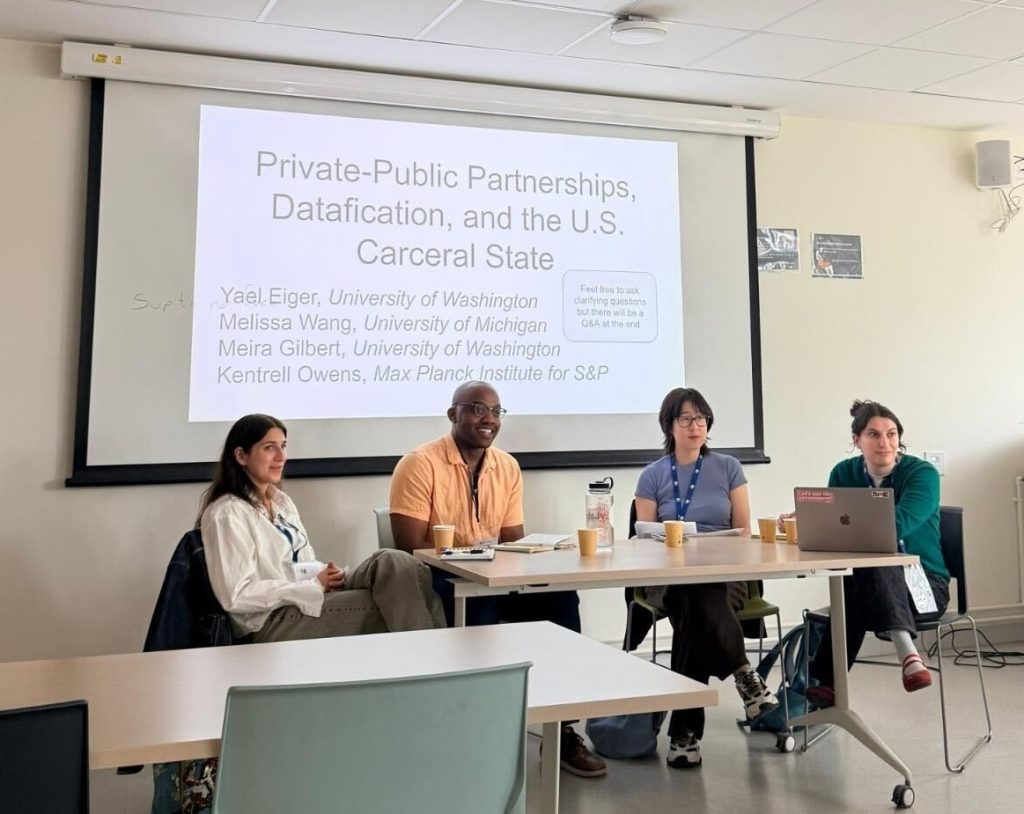
Security Lab PhD student Yael Eiger, Security Lab PhD alum Dr. Kentrell Owens, along with collaborators PhD student Meira Gilbert from the UW iSchool and PhD student Melissa Wang from the University of Michigan, attended the Surveillance Studies Conference to present a panel discussion on “Public-Privacy Partnerships, Datafication, and the U.S. Carceral State”.
Read Security Lab PhD student Yael Eiger‘s blog post on technology in Washington prisons over at the Washington History Project: The Desire and Disdain for Technology in WA Prisons. Yael’s dissertation work is exploring technology (especially harms) within the U.S. carceral system.
How do we anticipate and address security, privacy, and safety issues as technologies permeate society?
As technology permeates every aspect of our lives and societies, it has the potential to fundamentally change many things for the better. But realizing the potential benefits also requires sustained, thoughtful focus on the security, privacy, and safety risks that may and do arise from new technologies and their applications in new contexts. Anticipating, uncovering, documenting, mitigating, and avoiding such risks is an inter-disciplinary endeavor, requiring advances in technology, theory, design, law and policy — as well as in our understanding of how individuals and communities relate to technology. We bring together researchers and educators across the Allen School and the University of Washington whose work aims to lead us towards a safer, more secure, and more privacy-preserving future through technologies that ultimately better serve people and society.
Needless to say, we agree with the importance of this Grand Challenge! Read more here about the challenge and see all the great Allen School faculty involved in addressing this challenge, from the Security and Privacy Research Lab and beyond.
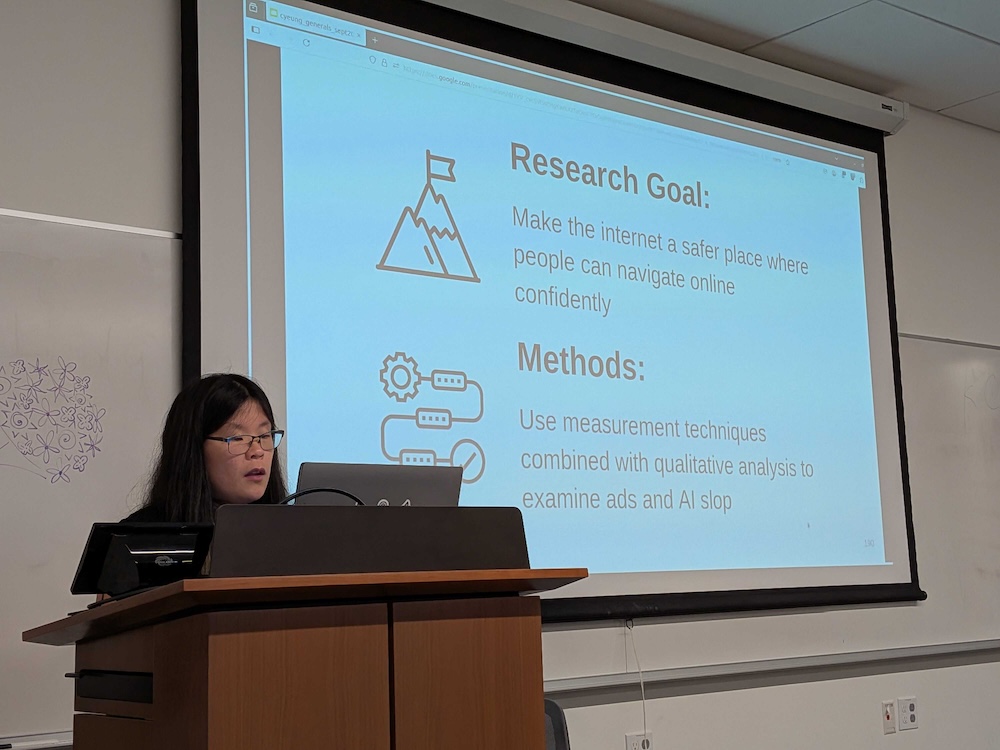
Congratulations to Security Lab PhD student — now PhD candidate — Tina Yeung! Tina just recently passed her General Exam (aka dissertation proposal), the last important official milestone in the Allen School PhD process before the final defense.
Back in 2011, a team of University of Washington and University of California San Diego researchers published a paper detailing how they could remotely hack into a pair of 2009 Chevy Impalas. By targeting a range of attack vectors including CD players, Bluetooth and cellular radio, the researchers were able to control multiple vehicle functions, from the windshield wipers to the brakes.
Since its publication, the team’s research has helped lead to new standards for motor vehicle security and put the brakes on automobile cyberattacks. For their lasting contributions, their paper titled “Comprehensive Experimental Analyses of Automotive Attack Surfaces” received the Test of Time Award at the 34th USENIX Security Symposium in Seattle earlier this month.
Franziska Roesner
“I was only a first-year graduate student when we started this project, and I had just switched my focus to security. It was such a privilege to be able to help out on such an important and impactful project, and to learn from all of the other members of the team about how to do this kind of research,” said co-author Franziska Roesner (Ph.D., ‘14), Brett Helsel Professor and co-director of the Security and Privacy Research Lab in the Allen School.
Modern automobiles are made up of independent computers called electronic control units (ECUs), typically connected through the Controller Area Network (CAN), that oversee different motor functions. In a previous paper, the team found that if an attacker physically connected to the car’s internal network could override critical safety systems. Building off of that work, the researchers analyzed the modern automobile’s external attack surface and found that an adversary could hack into a car from miles away.
The team identified three categories of components that were vulnerable to cyberattacks. An attacker could use an indirect physical channel such as tools that connect to the OBD-II port, which can access all CAN buses in the car, or through the media player. For example, the researchers compromised the car’s radio and then used a doctored CD to upload custom firmware. If an attacker is able to place a wireless transmitter in proximity to the car’s receiver, they can gain access to the ECU via Bluetooth or even remote keyless entry, the team found. Attackers do not have to be nearby to wreak havoc. Using long-range communication channels such as cellular, it is possible to exploit vulnerabilities in how the car’s telematics unit uses the aqLink code to remotely control the vehicle.
“More than 10 years ago, we saw that devices in our world were becoming incredibly computerized, and we wanted to understand what the risks might be if they continued to evolve without thought toward security and privacy,” said senior author Tadayoshi Kohno, who was then a professor at the Allen School, now faculty at Georgetown University, in a UW News release.
The impact of the team’s work can still be felt today. As a result of the research, car manufacturers including GM have hired entire security teams. The work has influenced the development of guidelines for original equipment manufacturers (OEMs) and also led to the creation of the Electronic Systems Safety Research Division at the National Highway Traffic Safety Administration. As cars grow increasingly more connected and autonomous, the insights from the UW and UCSD collaboration will continue to inform the automotive industry against emerging threats.
“Beyond the practical impact of the work, that experience has also made for great stories to tell in the computer security courses I teach now — for example, the time that we accidentally set the car’s horn to a permanent ‘on’ state while experimenting outside the Allen Center,” Roesner said.
Joining Roesner and Kohno at UW at the time of the original paper were Karl Koscher (Ph.D. ‘14), now a postdoc at UCSD, and Alexei Czeskis (Ph.D., ‘13), currently at LinkedIn. The original University of California San Diego group was made up of UCSD faculty members Stefan Savage (Ph.D., ‘02) and Hovav Shacham; Stephen Checkoway (B.S., ‘05), now faculty at Oberlin College; Damon McCoy, faculty at New York University; Danny Anderson, who runs a software consulting company; and late researcher Brian Kantor.
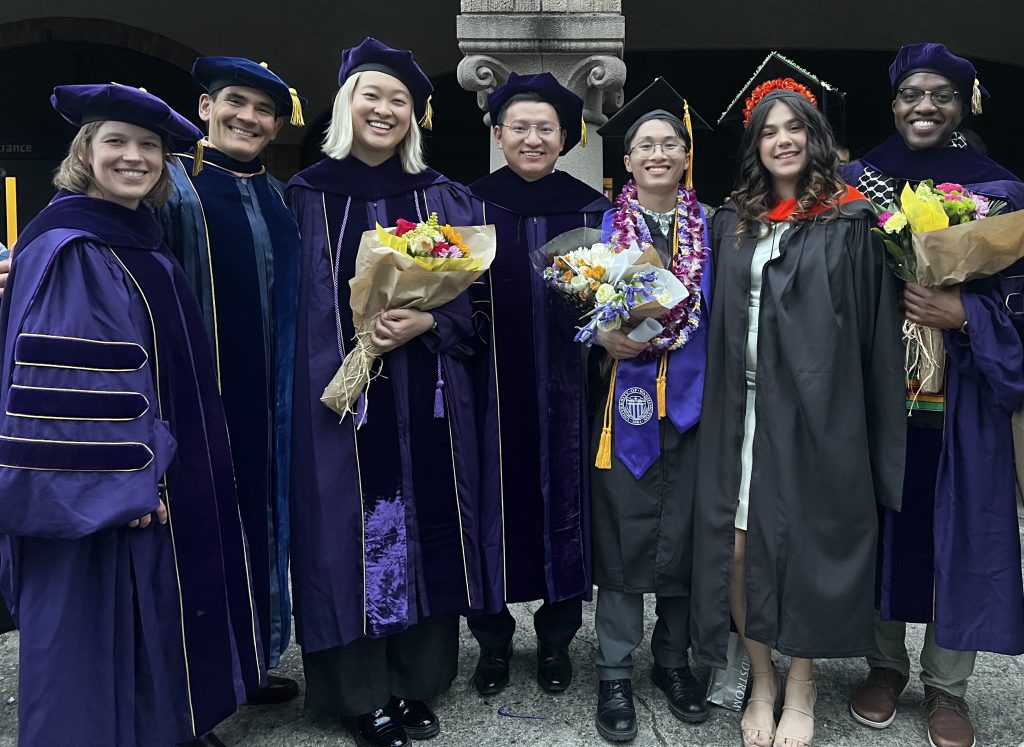
The UW Security Lab is so excited to congratulate our 2025 graduates!! It’s been an honor to work with all of you and we can’t wait to see where your careers lead you!
Left to right in the photo: Prof. Franzi Roesner, Prof. Yoshi Kohno, Dr. Miranda Wei (PhD graduate), Dr. Kaiming Cheng (PhD graduate), Evan Lam (BS graduate), Basia Radka (MS graduate), Dr. Kentrell Owens (PhD Graduate).